← 27 October 2026's Current Affairs · Science & Tech GA Prelims ★★★☆☆ Mains ★★☆☆☆
Kudankulam breach highlights cybersecurity gaps; CERT-In advisory in focus
ಸುದ್ದಿಯಲ್ಲಿ ಏಕೆ?
A nuclear plant breached beyond its fence: the CERT-In and Section 70B facts GS3 cyber security tests
Kudankulam breach and a CERT-In advisory spotlight India's cyber-defence gaps.
Why it matters: general awareness
What you need to know
2 ನಿಮಿಷ
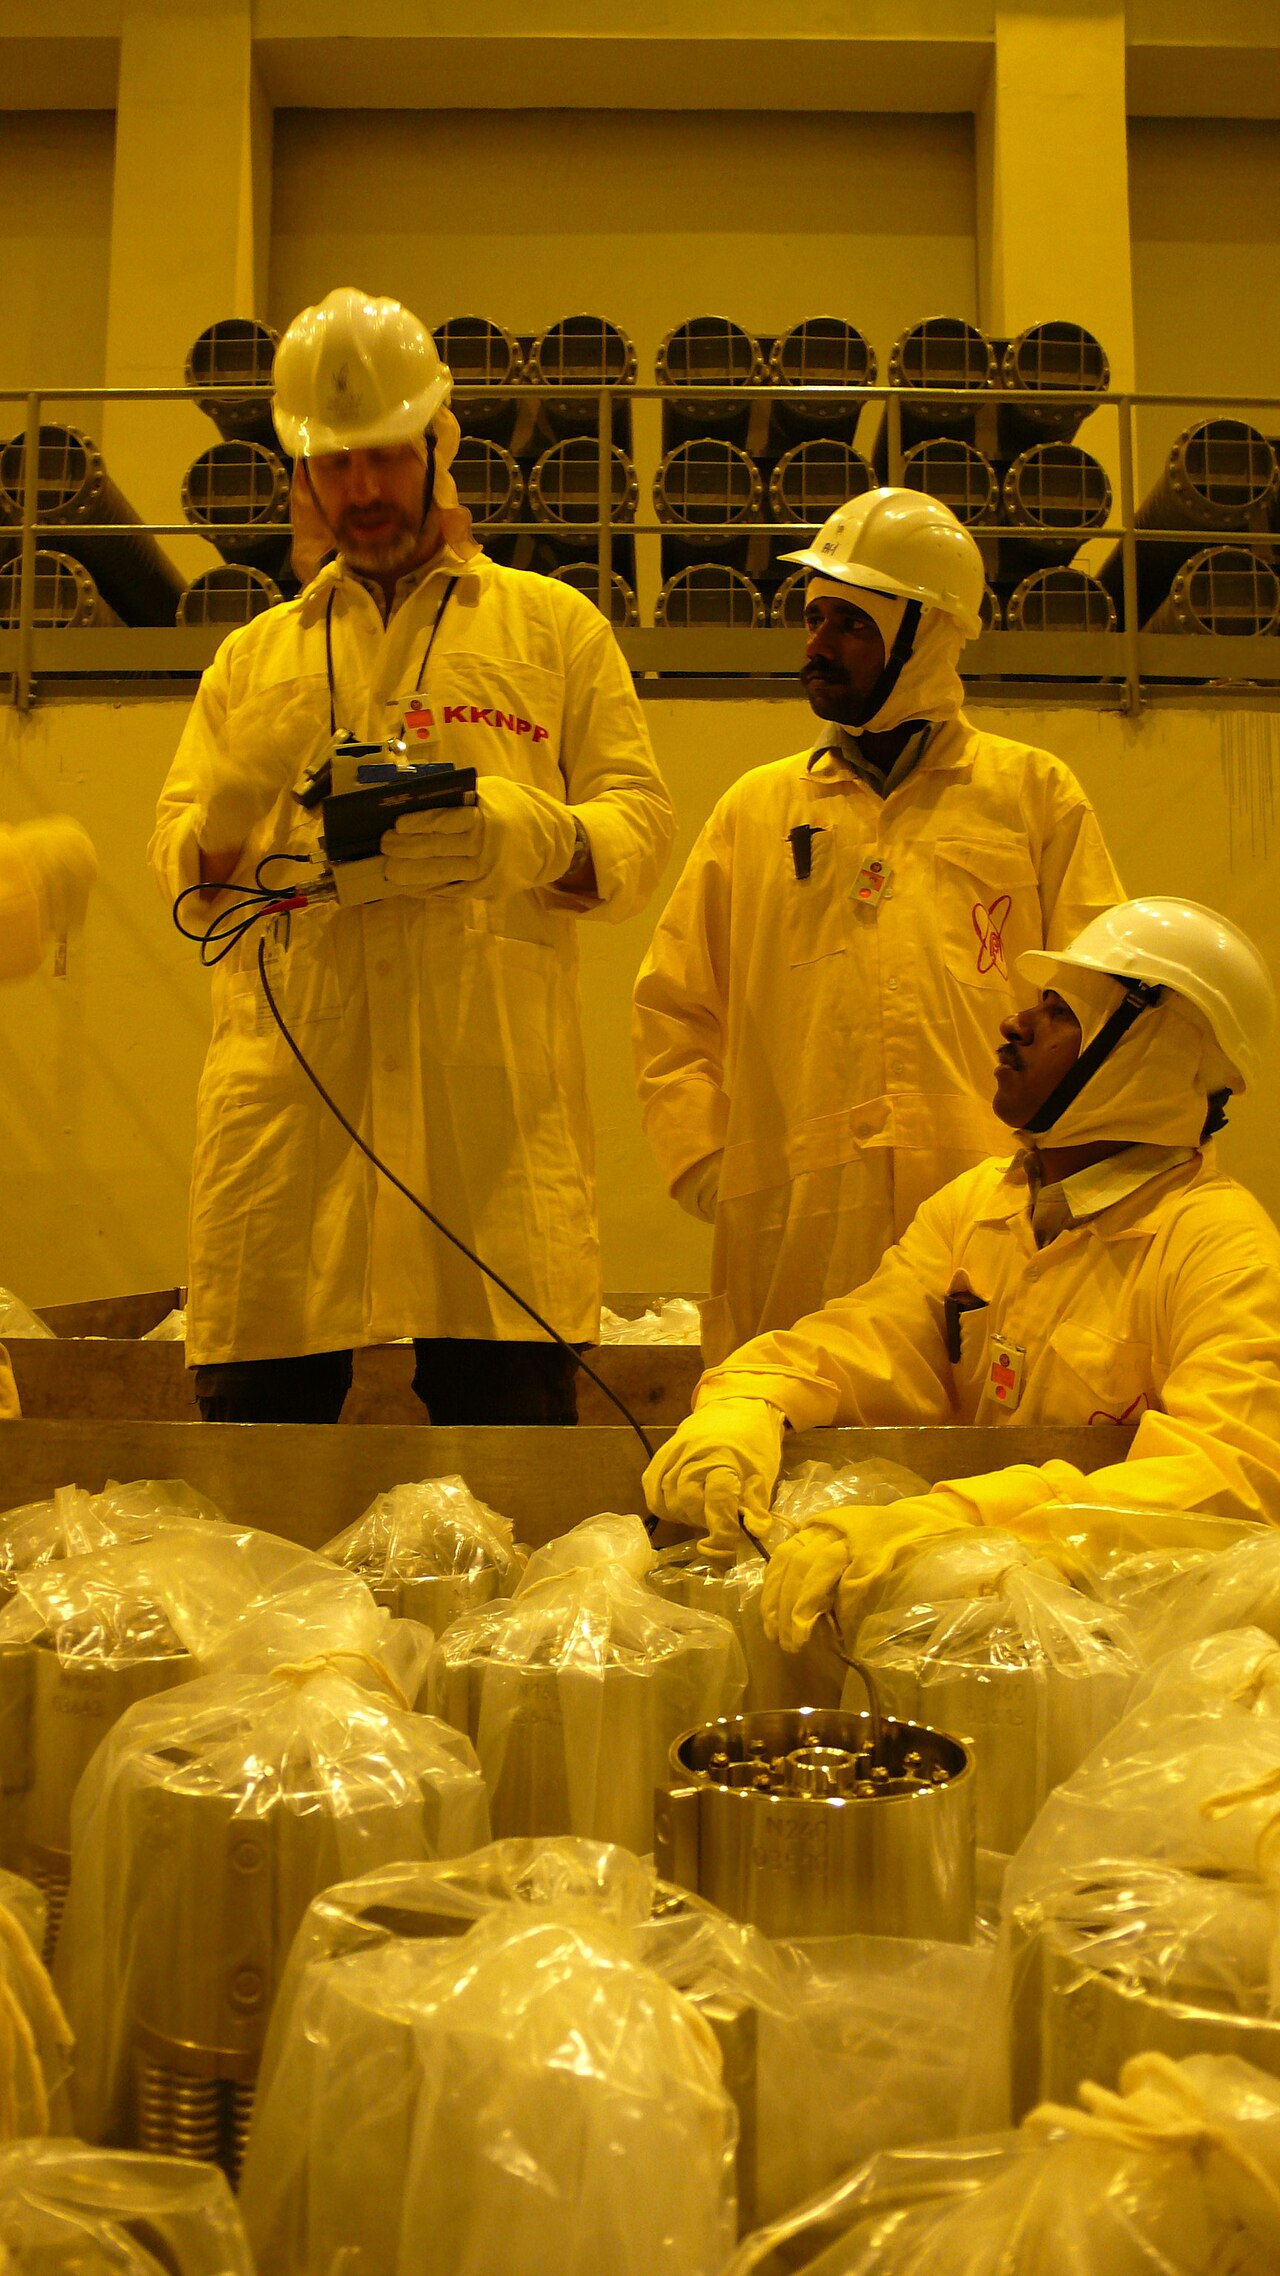
The Kudankulam breach has highlighted cybersecurity vulnerabilities that lie beyond the physical boundary of a nuclear plant, in its supply chain, networks and third-party systems.
A recent advisory by CERT-In underlines that India must do better at detecting and preventing data breaches.
CERT-In is the national agency for responding to cyber security incidents.
ಮೂಲಗಳು: Topper IAS editorial (PIB / The Hindu / Indian Express)
ಮುಖ್ಯ ಅಂಶಗಳು
Remember these
- Kudankulam breach exposed vulnerabilities in the supply chain, networks and third-party systems, beyond the plant's physical boundary
- CERT-In is India's national agency for responding to cyber security incidents
- CERT-In is designated under Section 70B of the Information Technology Act, 2000
- CERT-In works under the Ministry of Electronics and Information Technology (MeitY)
- A recent CERT-In advisory stresses better detection and prevention of data breaches
ಪ್ರಿಲಿಮ್ಸ್ · ಮೇನ್ಸ್
How the exam will ask it
ಪ್ರಿಲಿಮ್ಸ್
- CERT-In functions under the Ministry of Electronics and Information Technology.
- The statutory basis of CERT-In is Section 70B of the Information Technology Act, 2000.
- CERT-In is the national agency for responding to cyber security incidents.
- Kudankulam is a nuclear power plant in Tamil Nadu.
ಮೇನ್ಸ್
GS3 (Internal Security: cyber security). The Kudankulam breach shows that critical infrastructure is exposed through supply chains, networks and third-party systems, not only physical perimeters; the IT Act, 2000 and CERT-In advisories provide the framework. Way forward: mandatory incident reporting, vendor and supply-chain audits, sectoral CERTs and stronger capacity for detection and response.
Quick recall
Answer before you reveal
CERT-In ಬಗ್ಗೆ ಈ ಕೆಳಗಿನ ಹೇಳಿಕೆಗಳನ್ನು ಪರಿಗಣಿಸಿ:
- ಇದು ಎಲೆಕ್ಟ್ರಾನಿಕ್ಸ್ ಮತ್ತು ಮಾಹಿತಿ ತಂತ್ರಜ್ಞಾನ ಸಚಿವಾಲಯದ ಅಡಿ ಕಾರ್ಯನಿರ್ವಹಿಸುತ್ತದೆ.
- ಇದರ ಶಾಸನಬದ್ಧ ಆಧಾರ ಮಾಹಿತಿ ತಂತ್ರಜ್ಞಾನ ಕಾಯ್ದೆ, ೨೦೦೦ರ ಸೆಕ್ಷನ್ ೭೦ಬಿ. ಮೇಲಿನ ಹೇಳಿಕೆಗಳಲ್ಲಿ ಯಾವುದು/ಯಾವವು ಸರಿ?
- ೧ ಮಾತ್ರ
- ೨ ಮಾತ್ರ
- ೧ ಮತ್ತು ೨ ಎರಡೂ
- ೧ ಅಥವಾ ೨ ಯಾವುದೂ ಅಲ್ಲ
ಉತ್ತರ ನೋಡಿ
ಉತ್ತರ: C — ಸರಿಯಾದ ಉತ್ತರ ೧ ಮತ್ತು ೨ ಎರಡೂ. ಭಾರತೀಯ ಕಂಪ್ಯೂಟರ್ ತುರ್ತು ಪ್ರತಿಕ್ರಿಯಾ ತಂಡವು ಸೈಬರ್ ಭದ್ರತಾ ಘಟನೆಗಳ ರಾಷ್ಟ್ರೀಯ ಸಂಸ್ಥೆಯಾಗಿದ್ದು, ಐಟಿ ಕಾಯ್ದೆ ೨೦೦೦ರ ಸೆಕ್ಷನ್ ೭೦ಬಿ ಅಡಿ ಗೊತ್ತುಪಡಿಸಲಾಗಿದೆ ಮತ್ತು MeitY ಅಡಿ ಕೆಲಸ ಮಾಡುತ್ತದೆ.
Convert this topic into marks
Today's 10-MCQ test · instant analysis · Powered by AdaptIQ